

(Dec-2025) CCST-Networking Exam Dumps Contains FREE Real Quesions from the Actual Exam
Free Test Engine Verified By CCST Certified Experts
Cisco CCST-Networking Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
NEW QUESTION # 23
Which two pieces of information should you include when you initially create a support ticket? (Choose 2.)
- A. The description of the top-down fault-finding procedure
- B. A description of the conditions when the fault occurs
- C. A detailed description of the fault
- D. Details about the computers connected to the network
- E. The actions taken to resolve the fault
Answer: B,C
Explanation:
* Statement A: "A detailed description of the fault." This is essential for support staff to understand the nature of the problem and begin troubleshooting effectively.
* Statement C: "A description of the conditions when the fault occurs." This helps in reproducing the issue and identifying patterns that might indicate the cause of the fault.
* Statement B: "Details about the computers connected to the network." While useful, this is not as immediately critical as understanding the fault itself and the conditions under which it occurs.
* Statement D: "The actions taken to resolve the fault." This is important but typically follows the initial report.
* Statement E: "The description of the top-down fault-finding procedure." This is more of a troubleshooting methodology than information typically included in an initial support ticket.
References:
* Best Practices for Submitting Support Tickets: Support Ticket Guidelines
NEW QUESTION # 24
Move each cloud computing service model from the list on the left to the correct example on the right Note: You will receive partial credit for each correct answer.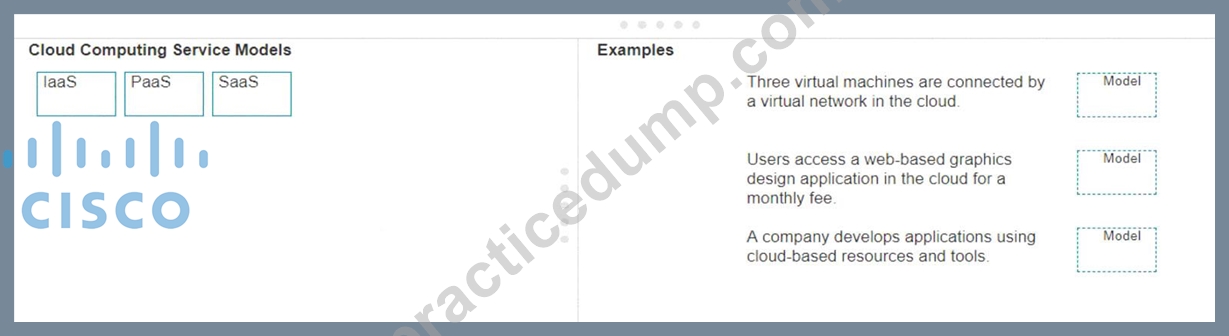
Answer:
Explanation:
Explanation:
* Three virtual machines are connected by a virtual network in the cloud.
* Model: IaaS (Infrastructure as a Service)
* Explanation: IaaS provides virtualized computing resources over the internet, including virtual machines, storage, and networks.
* Users access a web-based graphics design application in the cloud for a monthly fee.
* Model: SaaS (Software as a Service)
* Explanation: SaaS delivers software applications over the internet, typically on a subscription basis, accessible via a web browser.
* A company develops applications using cloud-based resources and tools.
* Model: PaaS (Platform as a Service)
* Explanation: PaaS provides a platform allowing customers to develop, run, and manage applications without dealing with the infrastructure.
* IaaS (Infrastructure as a Service): Provides virtualized hardware resources that customers can use to build their own computing environments.
* PaaS (Platform as a Service): Offers a platform with tools and services to develop, test, and deploy applications.
* SaaS (Software as a Service): Delivers fully functional applications over the internet that users can access and use without managing the underlying infrastructure.
References:
* Cloud Service Models: Understanding IaaS, PaaS, SaaS
* NIST Definition of Cloud Computing:NIST Cloud Computing
NEW QUESTION # 25
An engineer configured a new VLAN named VLAN2 for the Data Center team. When the teamtries to ping addresses outside VLAN2 from a computer in VLAN2, they are unable to reach them.
What should the engineer configure?
- A. Static route
- B. Default route
- C. Default gateway
- D. Additional VLAN
Answer: C
Explanation:
When devices within a VLAN are unable to reach addresses outside their VLAN, it typically indicates that they do not have a configured path to external networks. The engineer should configure a default gateway for VLAN2. The default gateway is the IP address of the router's interface that is connected to the VLAN, which will route traffic from the VLAN to other networks12.
References :=
*Understanding and Configuring VLAN Routing and Bridging on a Router Using the IRB Feature
*VLAN 2 not able to ping gateway - Cisco Community
*VLANs: Virtual Local Area Networks (VLANs) logically segment network traffic to improve security and performance. Devices within the same VLAN can communicate directly.
*Default Gateway: For devices in VLAN2 to communicate with devices outside their VLAN, they need a default gateway configured. The default gateway is typically a router or Layer 3 switch that routes traffic between different VLANs and subnets.
*Additional VLAN: Not needed in this scenario as the issue is related to routing traffic outside VLAN2, not creating another VLAN.
*Default Route: While a default route on the router may be necessary, the primary issue for devices within VLAN2 is to have a configured default gateway.
*Static Route: This is used on routers to manually specify routes to specific networks but does not address the need for a default gateway on the client devices.
References:
*Cisco VLAN Configuration Guide: Cisco VLAN Configuration
*Understanding and Configuring VLANs: VLANs Guide
NEW QUESTION # 26
What is the purpose of assigning an IP address to the management VLAN interface on a Layer 2 switch?
- A. To enable the switch to act as a default gateway for the attached devices
- B. To enable the switch to resolve URLs for the attached the devices
- C. To enable the switch to provide DHCP services to other switches in the network
- D. To enable access to the CLI on the switch through Telnet or SSH
Answer: D
Explanation:
The primary purpose of assigning an IP address to the management VLAN interface on a Layer 2 switch is to facilitate remote management of the switch. By configuring an IP address on the management VLAN, network administrators can access the switch's Command Line Interface (CLI) remotely using protocols such as Telnet or Secure Shell (SSH). This allows for convenient configuration changes, monitoring, and troubleshooting without needing physical access to the switch1.
References :=
*Understanding the Management VLAN
*Cisco - VLAN Configuration Guide
*Remote Management of Switches
Assigning an IP address to the management VLAN interface (often the VLAN 1 interface by default) on a Layer 2 switch allows network administrators to remotely manage the switch using protocols such as Telnet or SSH. This IP address does not affect the switch's ability to route traffic between VLANs but provides a means to access and configure the switch through its Command Line Interface (CLI).
*A: The switch does not act as a default gateway; this is typically a function of a Layer 3 device like a router.
*B: The switch does not resolve URLs; this is typically a function of DNS servers.
*C: The switch can relay DHCP requests but does not typically provide DHCP services itself; this is usually done by a dedicated DHCP server or router.
Thus, the correct answer is D. To enable access to the CLI on the switch through Telnet or SSH.
References :=
*Cisco VLAN Management Overview
*Cisco Catalyst Switch Management
NEW QUESTION # 27
Move each protocol from the list on the left to its correct example on the right.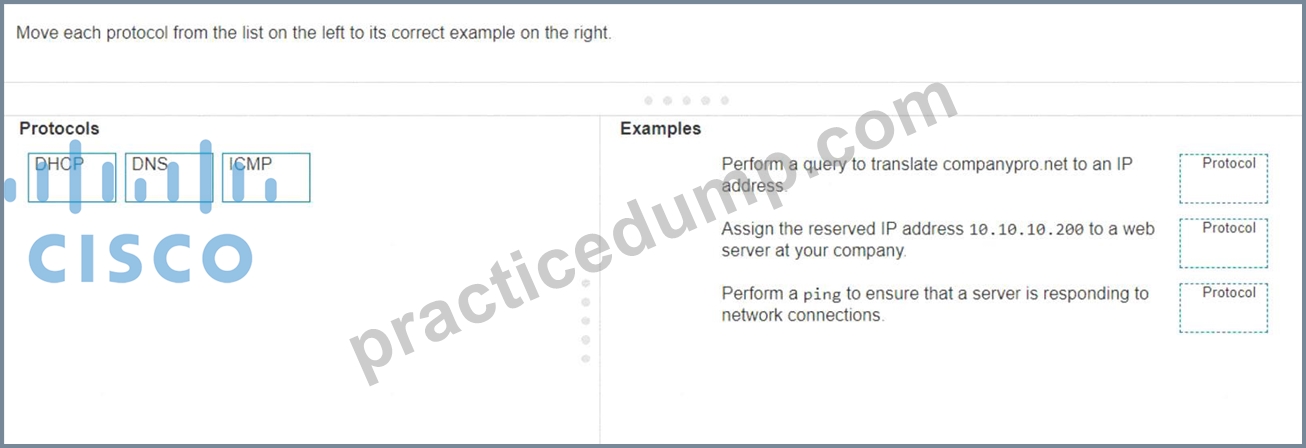
Answer:
Explanation:
Explanation:
The correct matching of the protocols to their examples is as follows:
* DHCP: Assign the reserved IP address 10.10.10.200 to a web server at your company.
* DNS: Perform a query to translate companypro.net to an IP address.
* ICMP: Perform a ping to ensure that a server is responding to network connections.
Here's how each protocol corresponds to its example:
* DHCP (Dynamic Host Configuration Protocol)is used to assign IP addresses to devices on a network. In this case, DHCP would be used to assign the reserved IP address 10.10.10.200 to a web server.
* DNS (Domain Name System)is used to translate domain names into IP addresses. Therefore, to translate companypro.net to an IP address, DNS would be utilized.
* ICMP (Internet Control Message Protocol)is used for sending error messages and operational information indicating success or failure when communicating with another IP address. An example of this is using the ping command to check if a server is responding to network connections.
These protocols are essential for the smooth operation of networks and the internet.
* Perform a query to translate companypro.net to an IP address.
* DNS (Domain Name System): DNS is used to resolve domain names to IP addresses.
* Assign the reserved IP address 10.10.10.200 to a web server at your company.
* DHCP (Dynamic Host Configuration Protocol): DHCP is used to assign IP addresses to devices on a network.
* Perform a ping to ensure that a server is responding to network connections.
* ICMP (Internet Control Message Protocol): ICMP is used by network devices to send error messages and operational information, and it is the protocol used by the ping command.
* DNS (Domain Name System): DNS translates human-friendly domain names like "companypro.net" into IP addresses that computers use to identify each other on the network.
* DHCP (Dynamic Host Configuration Protocol): DHCP automatically assigns IP addresses to devices on a network, ensuring that no two devices have the same IP address.
* ICMP (Internet Control Message Protocol): ICMP is used for diagnostic or control purposes, and the ping command uses ICMP to test the reachability of a host on an IP network.
References:
* DNS Basics: What is DNS?
* DHCP Overview: What is DHCP?
* ICMP and Ping: Understanding ICMP
NEW QUESTION # 28
Which device protects the network by permitting or denying traffic based on IP address, port number, or application?
- A. Intrusion detection system
- B. Firewall
- C. Access point
- D. VPN gateway
Answer: B
Explanation:
* Firewall: A firewall is a network security device that monitors and controls incoming and outgoing network traffic based on predetermined security rules. It permits or denies traffic based on IP addresses, port numbers, or applications.
* Access Point: This is a device that allows wireless devices to connect to a wired network using Wi-Fi.
It does not perform traffic filtering based on IP, port, or application.
* VPN Gateway: This device allows for secure connections between networks over the internet, but it is not primarily used for traffic filtering based on IP, port, or application.
* Intrusion Detection System (IDS): This device monitors network traffic for suspicious activity and policy violations, but it does not actively permit or deny traffic.
References:
* Understanding Firewalls: Firewall Basics
NEW QUESTION # 29
Which command will display all the current operational settings configured on a Cisco router?
- A. show protocols
- B. show startup-config
- C. show version
- D. show running-config
Answer: D
Explanation:
Router
Theshow running-configcommand is used on a Cisco router to display the current operational settings that are actively configured in the router's RAM. This command outputs all the configurations that are currently being executed by the router, which includes interface configurations, routing protocols, access lists, and other settings. Unlikeshow startup-config, which shows the saved configuration that the router will use on the next reboot,show running-configreflects the live, current configuration in use.
References:= The information is supported by multiple sources that detail the use of Cisco commands, particularly theshow running-configcommand as the standard for viewing the active configuration on a Cisco device123.
* show running-config: This command displays the current configuration running on the router. It includes all the operational settings and configurations applied to the router.
* show protocols: This command shows the status of configured protocols on the router but not the entire configuration.
* show startup-config: This command displays the configuration saved in NVRAM, which is used to initialize the router on startup, but not necessarily the current running configuration.
* show version: This command provides information about the router's software version, hardware components, and uptime but does not display the running configuration.
References:
* Cisco IOS Commands: Cisco IOS Commands
NEW QUESTION # 30
Examine the connections shown in the following image. Move the cable types on the right to the appropriate connection description on the left. You may use each cable type more than once or not at all.
Answer:
Explanation:
Explanation:
Based on the image description provided, here are the cable types matched with the appropriate connection descriptions:
Connects Switch S1 to Router R1 Gi0/0/1 interfaceCable Type: = Straight-through UTP Cable Connects Router R2 Gi0/0/0 to Router R3 Gi0/0/0 via underground conduitCable Type: = Fiber Optic Cable Connects Router R1 Gi0/0/0 to Router R2 Gi0/0/1Cable Type: = Crossover UTP Cable Connects Switch S3 to Server0 network interface cardCable Type: = Straight-through UTP Cable The choices are based on standard networking practices where:
* Straight-through UTP cablesare typically used to connect a switch to a router or a network interface card.
* Fiber optic cablesare ideal for long-distance, high-speed data transmission, such as connections through an underground conduit.
* Crossover UTP cablesare used to connect similar devices, such as router-to-router connections.
These matches are consistent with the color-coded cables in the image: green for switch connections, yellow for router-to-router connections within the same rack, and blue for inter-rack connections. The use of these cables follows the Ethernet cabling standards.
* Connects Switch S1 to Router R1 Gi0/0/1 interface:
* Cable Type: Straight-through UTP Cable
* Explanation: A straight-through UTP cable is typically used to connect different types of devices, such as a switch to a router.
* Connects Router R2 Gi0/0/0 to Router R3 Gi0/0/0 via underground conduit:
* Cable Type: Fiber Optic Cable
* Explanation: Fiber optic cables are used for long-distance connections, such as those through an underground conduit between buildings.
* Connects Router R1 Gi0/0/0 to Router R2 Gi0/0/1:
* Cable Type: Crossover UTP Cable
* Explanation: A crossover UTP cable is typically used to connect similar devices directly, such as router to router connections.
* Connects Switch S3 to Server0 network interface card:
* Cable Type: Straight-through UTP Cable
* Explanation: A straight-through UTP cable is typically used to connect a switch to an end device, such as a server.
* Straight-through UTP Cable: Used to connect different devices (e.g., switch to router, switch to server).
* Crossover UTP Cable: Used to connect similar devices directly (e.g., router to router, switch to switch).
* Fiber Optic Cable: Used for long-distance and high-speed connections, often between buildings or data centers.
References:
* Network Cable Types and Uses: Cisco Network Cables
* Understanding Ethernet Cabling: Ethernet Cable Guide
NEW QUESTION # 31
A user reports that a company website is not available. The help desk technician issues a tracert command to determine if the server hosting the website isreachable over the network. The output of the command is shown as follows:
What can you tell from the command output?
- A. Requests to the web server at 192.168.1.10 are being delayed and time out.
- B. The server with the address 192.168.1.10 is reachable over the network.
- C. The router at hop 3 is not forwarding packets to the IP address 192.168.1.10.
- D. The server address 192.168.1.10 is being blocked by a firewall on the router at hop 3.
Answer: B
Explanation:
The tracert command output shows the path taken to reach the destination IP address, 192.168.1.10. The command output indicates:
*Hops 1 and 2 are successfully reached.
*Hop 3 times out, meaning the router at hop 3 did not respond to the tracert request. However, this does not necessarily indicate a problem with forwarding packets, as some routers may be configured to block or not respond to ICMP requests.
*Hops 4 and 5 are successfully reached, with hop 5 being the destination IP 192.168.1.10, indicating that the server is reachable.
Thus, the correct answer is C. The server with the address 192.168.1.10 is reachable over the network.
References :=
*Cisco Traceroute Command
*Understanding Traceroute
The tracert command output indicates that the server with the address 192.168.1.10 is reachable over the network. The asterisk (*) at hop 3 suggests that the probe sent to that hop did not return a response, which could be due to a variety of reasons such as a firewall blocking ICMP packets or the router at that hop being configured not to respond to ICMP requests. However, since the subsequent hops (4 and 5) are showing response times, it means that the packets are indeed getting through and the server is reachable12.
References :=
*How to Use Traceroute Command to Read Its Results
*How to Use the Tracert Command in Windows
NEW QUESTION # 32
Which address is included in the 192.168.200.0/24 network?
- A. 192.168.201.13
- B. 192.168.200.13
- C. 192.168.199.13
- D. 192.168.1.13
Answer: B
Explanation:
*192.168.200.0/24 Network: This subnet includes all addresses from 192.168.200.0 to 192.168.200.255. The
/24 indicates a subnet mask of 255.255.255.0, which allows for 256 addresses.
*192.168.199.13: This address is in the 192.168.199.0/24 subnet, not the 192.168.200.0/24 subnet.
*192.168.200.13: This address is within the 192.168.200.0/24 subnet.
*192.168.201.13: This address is in the 192.168.201.0/24 subnet, not the 192.168.200.0/24 subnet.
*192.168.1.13: This address is in the 192.168.1.0/24 subnet, not the 192.168.200.0/24 subnet.
References:
*Subnetting Guide: Subnetting Basics
NEW QUESTION # 33
You need to connect a computer's network adapter to a switch using a 1000BASE-T cable.
Which connector should you use?
- A. RJ-11
- B. RJ-45
- C. OS2 LC
- D. Coax
Answer: B
Explanation:
*1000BASE-T Cable: This refers to Gigabit Ethernet over twisted-pair cables (Cat 5e or higher).
*Connector: RJ-45 connectors are used for Ethernet cables, including those used for 1000BASE-T.
*Coax: Used for cable TV and older Ethernet standards like 10BASE2.
*RJ-11: Used for telephone connections.
*OS2 LC: Used for fiber optic connections.
References:
*Ethernet Standards and Cables: Ethernet Cable Guide
NEW QUESTION # 34
A help desk technician receives the four trouble tickets listed below. Which ticket should receive the highest priority and be addressed first?
- A. Ticket 2: An online webinar is taking place in the conference room. The video conferencing equipment lost internet access.
- B. Ticket 3: A user reports that response time for a cloud-based application is slower than usual.
- C. Ticket 1: A user requests relocation of a printer to a different network jack in the same office. The jack must be patched and made active.
- D. Ticket 4: Two users report that wireless access in the cafeteria has been down for the last hour.
Answer: A
Explanation:
When prioritizing trouble tickets, the most critical issues affecting business operations or high-impact activities should be addressed first. Here's a breakdown of the tickets:
* Ticket 1: Relocation of a printer, while necessary, is not urgent and does not impact critical operations.
* Ticket 2: An ongoing webinar losing internet access is critical, especially if the webinar is time-sensitive and involves multiple participants.
* Ticket 3: Slower response time for a cloud-based application is important but typically not as urgent as a complete loss of internet access for a live event.
* Ticket 4: Wireless access down in the cafeteria affects users but does not have the same immediate impact as a live webinar losing connectivity.
Thus, the correct answer is B. Ticket 2: An online webinar is taking place in the conference room. The video conferencing equipment lost internet access.
References:=
* IT Help Desk Best Practices
* Prioritizing IT Support Tickets
NEW QUESTION # 35
In the network shown in the following graphic, Switch1 is a Layer 2 switch.
PC-A sends a frame to PC-C. Switch1 does not have a mapping entry for the MAC address of PC-C. Which action does Switch1 take?
- A. Switch1 queries Switch2 for the MAC address of PC-C.
- B. Switch1 sends an ARP request to obtain the MAC address of PC-C.
- C. Switch1 floods the frame out all active ports except port G0/1.
- D. Switch1 drops the frame and sends an error message back to PC-A.
Answer: C
Explanation:
Understanding How Layer 2 Switches Handle Unknown MAC Addresses
Switches operate atLayer 2 (Data Link Layer)of the OSI model and maintain aMAC address table (CAM table)to forward frames efficiently.
* When a switch receives a frame, itchecks its MAC address tableto see if it knows the destination MAC address.
* If the destinationMAC address is not in the table(meaning the switch does not know which port leads to PC-C), the switch follows theflooding behavior.
What Happens When Switch1 Receives a Frame from PC-A to PC-C?
* Switch1 checks its MAC table:
* The source MAC (PC-A) is recorded in the table on portG0/1.
* The destination MAC (PC-C)is not in the table.
* Switch1 does not know where PC-C is:
* Itfloodsthe frame out of allactive ports except the port it was received on (G0/1).
* This means the frame is sent to:
* Switch2 (via G0/23)
* PC-B (via G0/2)
* Switch2 receives the frame and follows the same process:
* If Switch2 has PC-C's MAC in its table, it forwards the frame appropriately.
* If not,it floodsthe frame again until PC-C replies.
* Once PC-C responds, Switch1 and Switch2 learn its MAC address and update their tables.
Why Other Options Are Incorrect:
#A. Switch1 queries Switch2 for the MAC address of PC-C.
* Incorrect:Switches do not query other switches directly for MAC addresses. Instead, they rely on learning MAC addresses dynamically through frame forwarding.
#B. Switch1 drops the frame and sends an error message back to PC-A.
* Incorrect:Switchesdo not drop frames for unknown MAC addresses. Instead, theyfloodthe frames out all ports except the incoming port.
#D. Switch1 sends an ARP request to obtain the MAC address of PC-C.
* Incorrect:
* ARP (Address Resolution Protocol)is only used to resolve IP addresses to MAC addresses.
* Since PC-A issending a frame (Layer 2), not an IP packet (Layer 3), ARP isnot involvedhere.
Conclusion
Since Switch1does not know the destination MAC address, itfloods the frame out all active ports except the port it was received on. This is the default behavior of Layer 2 switches when they encounter an unknown MAC address.
Thus, thecorrect answer is:#C. Switch1 floods the frame out all active ports except port G0/1.
References
* Cisco CCNA 200-301 Official Guide - MAC Address Table & Frame Forwarding
* RFC 894 - Standard for Ethernet Frame Forwarding
* Cisco Networking Essentials - Switch Flooding Behavior
NEW QUESTION # 36
Which standard contains the specifications for Wi-Fi networks?
- A. IEEE 802.3
- B. IEEE 802.11
- C. EIA/TIA 568A
- D. GSM
- E. LTE
Answer: B
Explanation:
The IEEE 802.11 standard contains the specifications for Wi-Fi networks. It is a set of media access control (MAC) and physical layer (PHY) specifications for implementing wireless local area network (WLAN) computer communication in various frequencies, including but not limited to 2.4 GHz, 5 GHz, and 6 GHz1.
This standard is maintained by the Institute of Electrical and Electronics Engineers (IEEE) and is commonly referred to as Wi-Fi. The standard has evolved over time to include several amendments that improve speed, range, and reliability of wireless networks.
References :=
*The Most Common Wi-Fi Standards and Types, Explained
*802.11 Standards Explained: 802.11ax, 802.11ac, 802.11b/g/n, 802.11a
*Wi-Fi Standards Explained - GeeksforGeeks
NEW QUESTION # 37
Examine the following output:
Which two conclusions can you make from the output of the tracert command? (Choose 2.) Note: You will receive partial credit for each correct answer.
- A. The IPv6 address associated with the www.cisco.com server is 2600:1408: c400: 38d: : b33.
- B. The trace successfully reached the www.cisco.com server.
- C. The routers at hops 5 and 6 are offline.
- D. The device sending the trace has IPv6 address 2600:1408:c400:38d :: b33.
- E. The trace failed after the fourth hop.
Answer: A,B
Explanation:
*Statement A: "The trace successfully reached the www.cisco.com server." This is true as indicated by the
"Trace complete" message at the end, showing that the trace has reached its destination.
*Statement C: "The IPv6 address associated with the www.cisco.com server is 2600:1408:c400:38d::b33." This is true because the final hop in the trace, which is the destination, has this IPv6 address.
*Statement B: "The trace failed after the fourth hop." This is incorrect as the trace continues beyond the fourth hop, despite some intermediate timeouts.
*Statement D: "The routers at hops 5 and 6 are offline." This is not necessarily true. The routers might be configured to not respond to traceroute requests.
*Statement E: "The device sending the trace has IPv6 address 2600:1408:c400:38d::b33." This is incorrect; this address belongs to the destination server, not the sender.
References:
*Understanding Traceroute: Traceroute Guide
NEW QUESTION # 38
Which device protects the network by permitting or denying traffic based on IP address, port number, or application?
- A. Intrusion detection system
- B. Firewall
- C. Access point
- D. VPN gateway
Answer: B
Explanation:
* Firewall: A firewall is a network security device that monitors and controls incoming and outgoing network traffic based on predetermined security rules. It permits or denies traffic based on IP addresses, port numbers, or applications.
* Access Point: This is a device that allows wireless devices to connect to a wired network using Wi-Fi. It does not perform traffic filtering based on IP, port, or application.
* VPN Gateway: This device allows for secure connections between networks over the internet, but it is not primarily used for traffic filtering based on IP, port, or application.
* Intrusion Detection System (IDS): This device monitors network traffic for suspicious activity and policy violations, but it does not actively permit or deny traffic.
References:
* Understanding Firewalls: Firewall Basics
NEW QUESTION # 39
You need to connect a computer's network adapter to a switch using a 1000BASE-T cable.
Which connector should you use?
- A. RJ-11
- B. RJ-45
- C. OS2 LC
- D. Coax
Answer: B
Explanation:
*1000BASE-T Cable: This refers to Gigabit Ethernet over twisted-pair cables (Cat 5e or higher).
*Connector: RJ-45 connectors are used for Ethernet cables, including those used for 1000BASE-T.
*Coax: Used for cable TV and older Ethernet standards like 10BASE2.
*RJ-11: Used for telephone connections.
*OS2 LC: Used for fiber optic connections.
References:
*Ethernet Standards and Cables: Ethernet Cable Guide
NEW QUESTION # 40
During the data encapsulation process, which OSI layer adds a header that contains MAC addressing information and a trailer used for error checking?
- A. Network
- B. Transport
- C. Session
- D. Data Link
Answer: D
Explanation: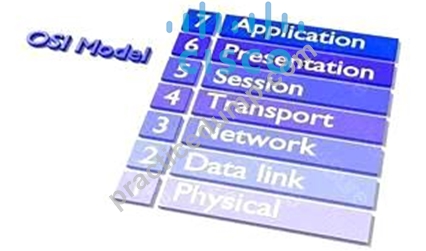
OSI model
During the data encapsulation process, theData Link layerof the OSI model is responsible for adding a header that contains MAC addressing information and a trailer used for error checking.The header typically includes the source and destination MAC addresses, while the trailer contains a Frame Check Sequence (FCS) which is used for error detection1.
The Data Link layer ensures that messages are delivered to the proper device on a LAN using hardware addresses and translates messages from the Network layer into bits for the Physical layer to transmit. It also controls how data is placed onto the medium and is received from the medium through the physical hardware.
References:=
* The OSI Model - The 7 Layers of Networking Explained in Plain English
* OSI Model - Network Direction
* Which layer adds both header and trailer to the data?
* What is OSI Model | 7 Layers Explained - GeeksforGeeks
NEW QUESTION # 41
Move each protocol from the list on the left to the correct TCP/IP model layer on the right.
Note: You will receive partial credit for each correct match.
Answer:
Explanation:
Explanation:
Here's how each protocol aligns with the correct TCP/IP model layer:
* TCP (Transmission Control Protocol): This protocol belongs to theTransportlayer, which is responsible for providing communication between applications on different hosts1.
* IP (Internet Protocol): IP is part of theInternetworklayer, which is tasked with routing packets across network boundaries to their destination1.
* FTP (File Transfer Protocol): FTP operates at theApplicationlayer, which supports application and end-user processes.It is used for transferring files over the network1.
* Ethernet: While not a protocol within the TCP/IP stack, Ethernet is associated with theNetwork Interfacelayer, which corresponds to the link layer of the TCP/IP model and is responsible for the physical transmission of data1.
The TCP/IP model layers are designed to work collaboratively to transmit data from one layer to another, with each layer having specific protocols that perform functions necessary for the data transmission process1.
* TCP:
* TCP Model Layer: Transport
* Explanation: The Transport layer is responsible for end-to-end communication and error handling. TCP (Transmission Control Protocol) operates at this layer to provide reliable, ordered, and error-checked delivery of data.
* IP:
* TCP Model Layer: Internetwork
* Explanation: The Internetwork layer, also known as the Internet layer, is responsible for logical addressing and routing. IP (Internet Protocol) operates at this layer to route packets across networks.
* FTP:
* TCP Model Layer: Application
* Explanation: The Application layer provides network services to applications. FTP (File Transfer Protocol) operates at this layer to transfer files between computers over a network.
* Ethernet:
* TCP Model Layer: Network
* Explanation: The Network layer, also known as the Link layer in the TCP/IP model, is responsible for physical addressing and access to the physical medium. Ethernet operates at this layer to provide the physical and data link functions.
* Transport Layer: This layer is responsible for providing communication services directly to the application processes running on different hosts. TCP is a core protocol in this layer.
* Internetwork Layer: This layer is responsible for logical addressing, routing, and packet forwarding.
IP is the primary protocol for this layer.
* Application Layer: This layer interfaces directly with application processes and provides common network services. FTP is an example of a protocol operating in this layer.
* Network Layer: In the TCP/IP model, this layer includes both the data link and physical layers of the OSI model. Ethernet is a protocol used in this layer to define network standards and communication protocols at the data link and physical levels.
References:
* TCP/IP Model Overview: Cisco TCP/IP Model
* Understanding the TCP/IP Model: TCP/IP Layers
NEW QUESTION # 42
Move the MFA factors from the list on the left to their correct examples on the right. You may use each factor once, more than once, or not at all.
Note: You will receive partial credit for each correct selection.
Answer:
Explanation:
Explanation:
The correct matching of the MFA factors to their examples is as follows:
* Entering a one-time security code sent to your device after logging in: Possession
* Holding your phone to your face to be recognized: Inherence
* Specifying your user name and password to log on to a service: Knowledge Here's why each factor matches the example:
* Possession: This factor is something the user has, like a mobile device. A one-time security code sent to this device falls under this category.
* Inherence: This factor is something the user is, such as a biometric characteristic. Facial recognition using a phone is an example of this factor.
* Knowledge: This factor is something the user knows, like a password or PIN.
Multi-Factor Authentication (MFA) enhances security by requiring two or more of these factors to verify a user's identity before granting access.
* Entering a one-time security code sent to your device after logging in.
* Factor: Possession
* Explanation: This factor relates to something you have, such as a device that receives a security code.
* Holding your phone to your face to be recognized.
* Factor: Inference (typically referred to as Inherence or Biometric)
* Explanation: This factor relates to something you are, such as biometric authentication like facial recognition.
* Specifying your username and password to log on to a service.
* Factor: Knowledge
* Explanation: This factor relates to something you know, such as a username and password.
* Possession Factor: This involves something the user has in their possession. Receiving a one-time security code on a device (e.g., phone) is an example of this.
* Inference Factor (Inherence/Biometric): This involves something inherent to the user, such as biometric verification (e.g., facial recognition or fingerprint scanning).
* Knowledge Factor: This involves something the user knows, such as login credentials (username and password).
References:
* Multi-Factor Authentication (MFA) Explained: MFA Guide
* Understanding Authentication Factors: Authentication Factors
NEW QUESTION # 43
You purchase a new Cisco switch, turn it on, and connect to its console port. You then run the following command:
For each statement about the output, select True or False.
Note: You will receive partial credit for each correct selection.
Answer:
Explanation:
Explanation:
* The two interfaces are administratively shut down:
* False: The output does not show any "shutdown" command under the interfaces, which would indicate that they are administratively shut down. Therefore, they are likely in their default state, which is administratively up.
* The two interfaces have default IP addresses assigned:
* False: The output does not show any IP address configuration. In the default state, interfaces do not have IP addresses assigned unless explicitly configured.
* The two interfaces can communicate over Layer 2:
* True: By default, interfaces on a switch are Layer 2 interfaces capable of forwarding Ethernet frames. As there is no configuration provided that changes this, it can be assumed they can communicate over Layer 2.
* Interface Status: The absence of the "shutdown" command means the interfaces are not administratively shut down.
* IP Address Assignment: There is no evidence in the output that IP addresses have been assigned to the interfaces, which would typically be shown as "ip address" entries.
* Layer 2 Communication: Switch interfaces in their default state operate at Layer 2, enabling them to forward Ethernet frames and participate in Layer 2 communication.
References:
* Cisco IOS Interface Configuration: Cisco Interface Configuration
* Understanding Cisco Switch Interfaces: Cisco Switch Interfaces
NEW QUESTION # 44
A support technician examines the front panel of a Cisco switch and sees 4 Ethernet cables connected in the first four ports. Ports 1, 2, and 3 have a green LED. Port 4 has a blinking green light.
What is the state of the Port 4?
- A. Link is up and active.
- B. Link is up with cable malfunctions.
- C. Link is up and there is no activity.
- D. Link is up and not stable.
Answer: A
NEW QUESTION # 45
During the data encapsulation process, which OSI layer adds a header that contains MAC addressing information and a trailer used for error checking?
- A. Network
- B. Transport
- C. Session
- D. Data Link
Answer: D
NEW QUESTION # 46
......
Use Real Cisco Achieve the CCST-Networking Dumps - 100% Exam Passing Guarantee: https://pass4sure.practicedump.com/CCST-Networking-exam-questions.html