

The Most In-Demand Fortinet FCP_GCS_AD-7.6 Pass Guaranteed Quiz
New Version FCP_GCS_AD-7.6 Certificate & Helpful Exam Dumps is Online
Fortinet FCP_GCS_AD-7.6 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
| Topic 7 |
|
| Topic 8 |
|
| Topic 9 |
|
| Topic 10 |
|
| Topic 11 |
|
| Topic 12 |
|
| Topic 13 |
|
| Topic 14 |
|
NEW QUESTION # 14
Refer to the exhibit.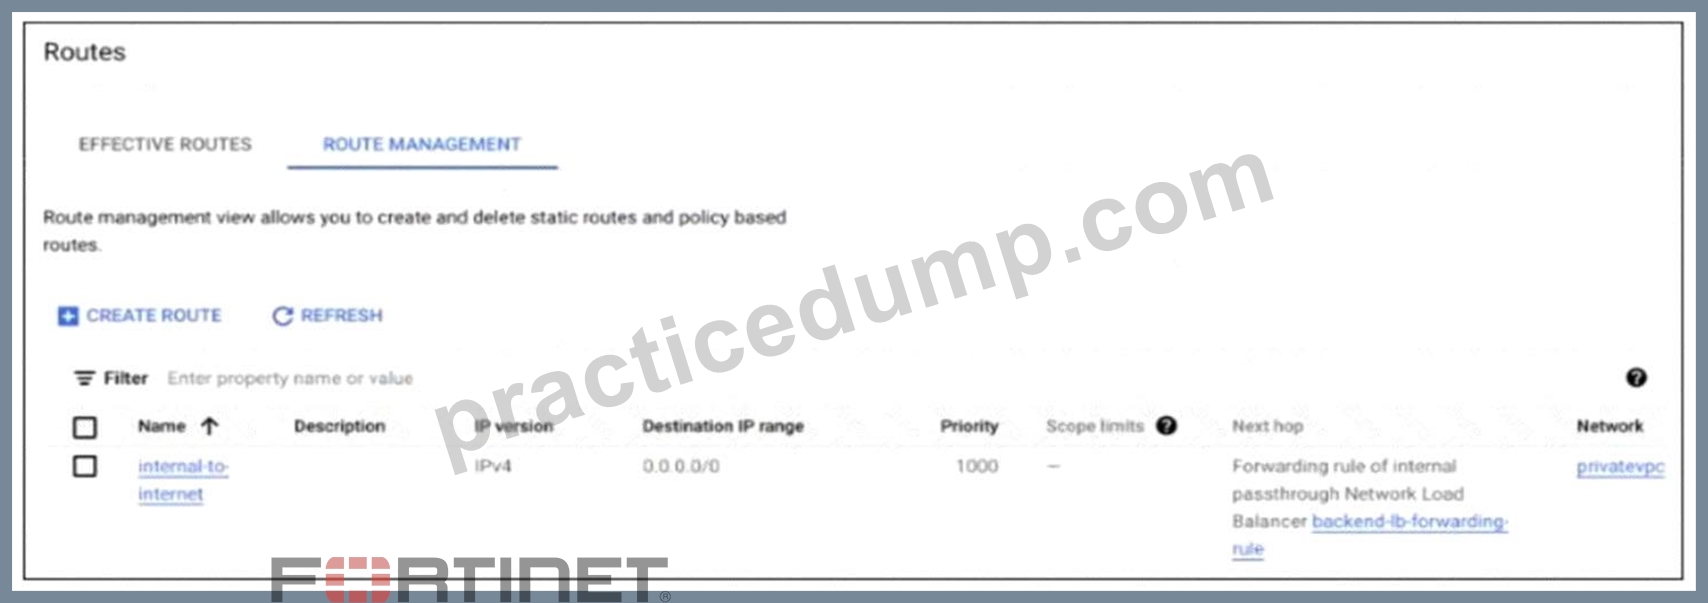
Which three conclusions can you draw from the Google Cloud custom route? (Choose three.)
- A. Atarget pool-based passthrough network load balancer was created.
- B. At least one instance group was created.
- C. A health check was created.
- D. A group-based passthrough network load balancer was created.
- E. The next hop must be updates manually in the custom route if the current next hop goes down.
Answer: B,C,E
Explanation:
The route's next hop is a forwarding rule for a backend service, which indicates a group-based passthrough load balancer.
Group-based load balancers require health checks to monitor instance health.
Backend services attach to instance groups to distribute traffic, so at least one instance group exists.
NEW QUESTION # 15
Refer to the exhibit.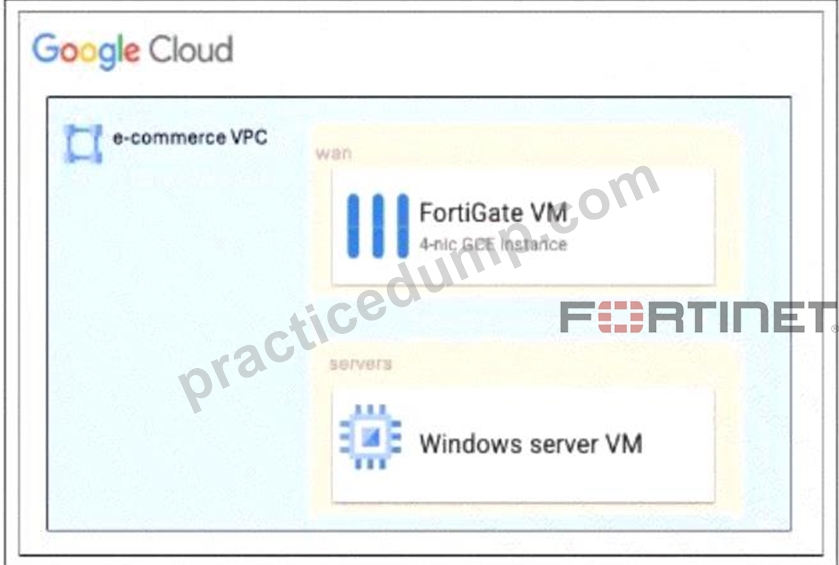
An administrator is troubleshooting network connectivity issues between two VMs deployed in Google Cloud.
One VM is a FortiGate located in the subnet "wan" that is part of the VPC "e-commerce". The other VM is a Windows server located in subnet "servers", which is also in the "e-commerce" VPC.
What are two reasons you cannot pint the Windows server from FortiGate? (Choose two.)
- A. The default Google Cloud firewall policy does not allow this traffic.
- B. The Windows firewall is blocking the traffic.
- C. ICMP traffic is blocked between Google Cloud subnets by default.
- D. Add a Google Cloud firewall rule to allow ICMP traffic inbound to the Windows firewall VM.
Answer: B,D
Explanation:
Google Cloud firewall rules are stateful and, by default, do not allow ICMP traffic; you must explicitly allow ICMP inbound traffic to the Windows VM.
The Windows VM's own firewall might block ICMP traffic, preventing ping responses.
NEW QUESTION # 16
Refer to the exhibit.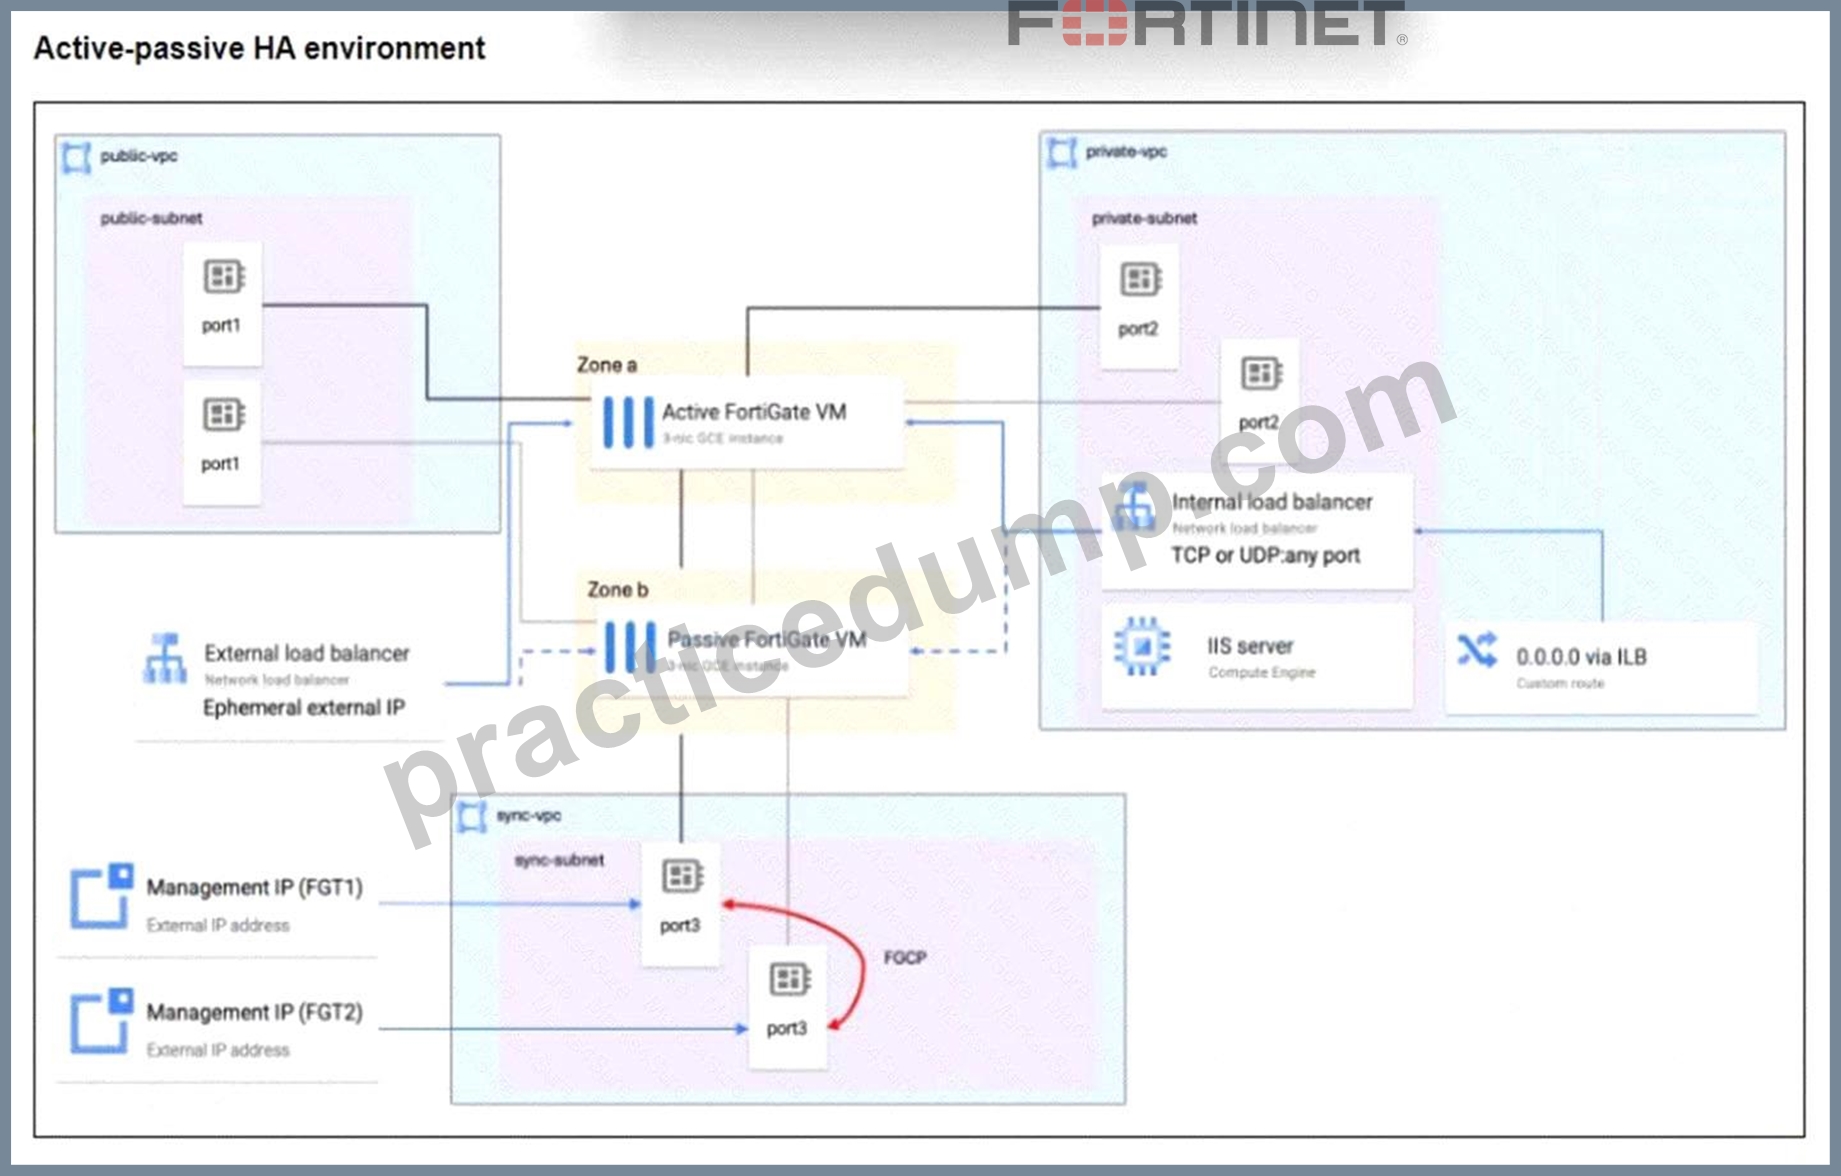
Which three things happen during a failover in which the passive FortiGate VM becomes the master cluster member in an active-passive high-availability (HA) environment? (Choose three.)
- A. The Management IP address moves from port3 of the current active member to port3 of the new active cluster member.
- B. The health check ensures that incoming traffic to the ephemeral external IP address of the load balancer is forwarded to the new active cluster member.
- C. The health check status will indicate that the old active cluster member is unhealthy.
- D. The health check for the passthrough load balancers forces internal traffic to route to port2 of the new active cluster member.
- E. The custom route is updated using API calls to forward all traffic to port2 of the new active cluster member device.
Answer: B,C,E
Explanation:
The load balancer health check detects the failure of the old active member and forwards traffic to the new active member.
The health check reflects the status change, marking the previous active as unhealthy.
API calls update custom routes to redirect traffic to the new active cluster member's internal interface (port2).
NEW QUESTION # 17
An administrator has been tasked with modifying their organization's existing active-passive high-availability (HA) FortiGate cluster and turn it into an active-active HA cluster.
Which two behavior changes will the administrator see in the cluster after the change? (Choose two.)
- A. The cluster no longer act as a single logical instance.
- B. The configuration will no longer be synchronized between cluster members.
- C. There is no longer a need to reserve a dedicated port for HA communications.
- D. The sessions will no longer be synchronized between cluster members.
Answer: A,C
Explanation:
Active-active HA does not require a dedicated HA communication port as each member handles traffic independently.
In active-active mode, cluster members operate more independently and do not present as a single logical device like in active-passive mode.
NEW QUESTION # 18
Google Cloud network services offer vast functionality and inter-connectivity between the cloud and on- premises networks.
Which three additional functions does FortiGate offer when deployed in Google Cloud to complement the native services offered by Google Cloud? (Choose three.)
- A. Web filtering
- B. SSL VPN
- C. OSPF over IPSec
- D. Secure SD-WAN with application visibility
- E. SSL inspection
Answer: B,D,E
Explanation:
FortiGate provides SSL VPN capabilities for secure remote access.
It offers SSL inspection to decrypt and inspect encrypted traffic for threats.
FortiGate supports Secure SD-WAN with deep application visibility and control, enhancing network performance and security beyond native Google Cloud services.
NEW QUESTION # 19
What are the two responsibilities of a Google Cloud customer in terms of security? (Choose two.)
- A. The Google Cloud customer is responsible for securing operating systems and applications.
- B. The Google Cloud customer is responsible for securing network traffic.
- C. The Google Cloud customer is responsible for securing the computing resources.
- D. The Google Cloud customer is responsible for securing cloud storage infrastructure.
Answer: A,B
Explanation:
Customers manage security for their data, applications, operating systems, and network configurations, while Google secures the underlying cloud infrastructure.
NEW QUESTION # 20
You have been tasked with destroying all resources relating to a recent active-active high-availability (HA) FGSP Terraform deployment in Google Cloud.
What steps do you have to take to ensure a successful deletion? (Choose two.)
- A. Delete all resources manually because active-active HA clusters cannot be destroyed using Terraform.
- B. Use the command terraform plan before destroying the Terraform template.
- C. Use the command terraform destroy to delete all resources deployed by the Terraform template.
- D. Delete all dependencies to resources relating to the Terraform template.
Answer: C,D
Explanation:
Removing dependencies prevents resource conflicts during deletion.
terraform destroy is the correct command to cleanly and completely remove all resources created by the Terraform deployment.
NEW QUESTION # 21
You need to deploy a new Windows server in Google Cloud to offload web traffic from an existing web server in a different zone.
As the customer, which two actions must you take to secure the new ComputeEngine instance? (Choose two.)
- A. Assign firewall rules to the compute engine instance.
- B. Implement a web application firewall.
- C. Change the proxy load balancer to an application load balancer.
- D. Configure Google Cloud IAM to limit Windows administrator access.
Answer: A,D
Explanation:
Assigning firewall rules controls network traffic to the instance, protecting it from unauthorized access.
Configuring IAM to limit administrative access ensures only authorized users can manage the Windows server, enhancing security.
NEW QUESTION # 22
An organization has decided to deploy an active-active high-availability cluster in Google Cloud.
Which three load balancing features are critical to the successful deployment of the cluster? (Choose three.)
- A. The symmetric hashing of the internal passthrough network load balancer
- B. The session termination of the external passthrough network load balancer
- C. The health check used by the internal and the external passthrough network load balancer
- D. The forwarding rule for the internal passthrough network load balancer as the next hot for custom routes
- E. The L3_DEFAULT protocol in the forwarding rule of the internal passthrough network load balancer
Answer: A,C,D
Explanation:
Health checks ensure load balancers route traffic only to healthy cluster members.
Forwarding rules act as next hops in routing, directing traffic appropriately within the HA cluster.
Symmetric hashing ensures consistent and balanced traffic distribution across cluster members, critical for active-active deployments.
NEW QUESTION # 23
An organization is planning to deploy two FortiGate VMs in two different regions.
Which two Google Cloud core components can span both FortiGate VMs in both regions? (Choose two.)
- A. Google Cloud project
- B. Google Cloud virtual private cloud
- C. Google Cloud zone
- D. Google Cloud subnet
Answer: A,B
Explanation:
A Google Cloud VPC can span multiple regions, allowing FortiGate VMs in different regions to be part of the same network.
A Google Cloud project provides the administrative boundary that can include resources across multiple regions and VPCs, enabling centralized management of both FortiGate VMs.
NEW QUESTION # 24
Refer to the exhibit.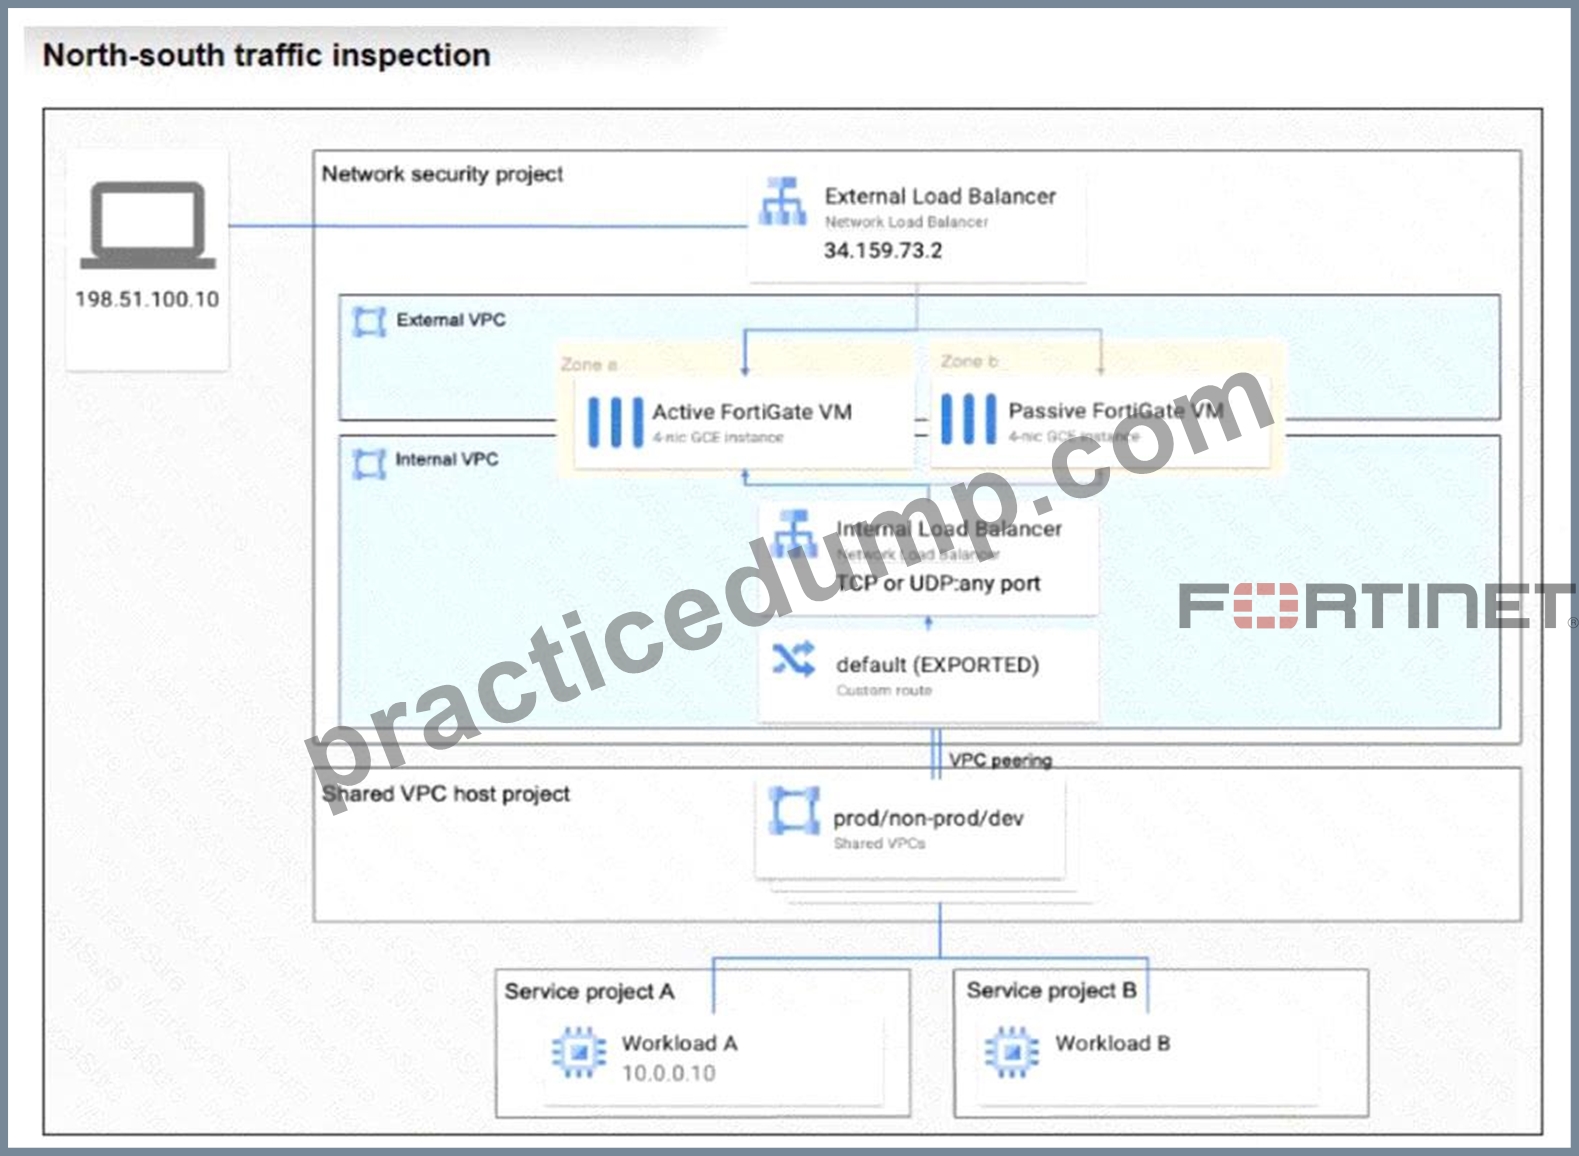
Which two types of traffic flow must the FortiGate cluster inspect, if the client at 198.51.100.10 sends traffic to the Workload A instance? (Choose two.)
- A. West-bound
- B. East-bound
- C. North-bound
- D. South-bound
Answer: B,D
Explanation:
South-bound traffic refers to traffic coming from outside the network (the client 198.51.100.10) into the internal environment.
East-bound traffic refers to traffic moving laterally within the internal network, such as between VPCs or workloads, which the FortiGate cluster can inspect for internal threats.
NEW QUESTION # 25
Refer to the exhibit.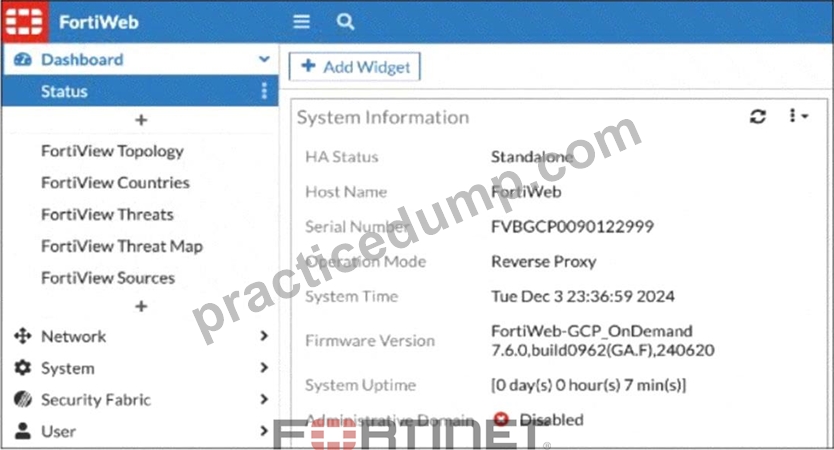
Which two statements about FortiWeb instances deployed in Google Cloud are true?
- A. You can configure the FortiWeb instance with only one network interface.
- B. By default, you can access FortiWeb using HTTPS on port 443.
- C. You can change the operation mode of FortiWeb.
- D. You can deploy FortiWeb using pay-as-you-go or bring-your-own-license.
Answer: C,D
Explanation:
FortiWeb's operation mode can be changed, such as between reverse proxy and transparent modes, to suit different deployment scenarios.
FortiWeb in Google Cloud supports flexible licensing models, including pay-as-you-go and bring-your-own- license (BYOL).
NEW QUESTION # 26
Refer to the exhibit.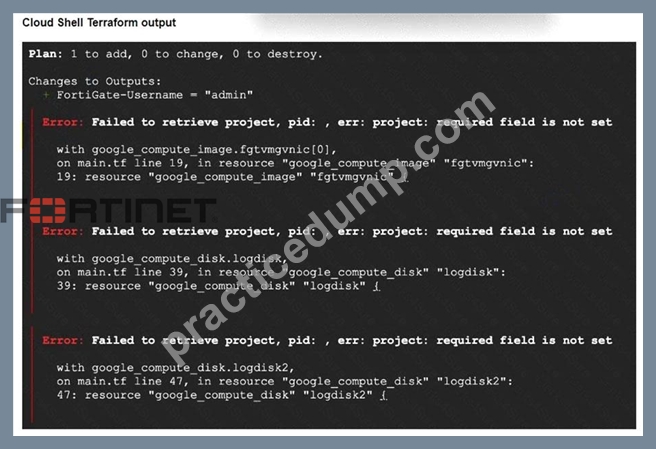
An administrator is attempting to deploy a Terraform template using Google Cloud Shell.
Which step must the administrator take to solve the error?
- A. Manually create a Google Cloud storage bucket for logging functionality.
- B. Use the command terraform init to initialize the Terraform directory.
- C. Use the command gcloud config set project to set the Google Cloud project in Google Cloud Shell.
- D. Delete the admin user to proceed with the Terraform script.
Answer: C
Explanation:
The error indicates the Google Cloud project is not set, which is required for Terraform to access resources.
Setting the project with gcloud config set project [PROJECT_ID] resolves this by specifying the active project in Cloud Shell.
NEW QUESTION # 27
Your organization has deployed an active-active high-availability (HA) FortiGate cluster in Google Cloud.
You have noticed a significant increase in asymmetrical traffic flow.
Which two actions can you take to mitigate the issue? (Choose two.)
- A. Enable source NAT for ingress traffic.
- B. Enable destination NAT for ingress traffic.
- C. Enable the layer 3 unified threat management (UTM) scanning feature if the FortiGate devices are on ForiOS 6.4 or later.
- D. Enable symmetric hashing on the external load balancer.
Answer: A,D
Explanation:
Enabling source NAT ensures consistent source IPs, promoting symmetric traffic flow.
Symmetric hashing on the load balancer helps distribute traffic flows evenly and consistently across cluster members, reducing asymmetric routing.
NEW QUESTION # 28
You are tasked with deploying a load balancer in Google Cloud that does not terminate sessions arriving from outside the VPC and that forwards traffic to the organization's internal web servers.
Which load balancer type should you deploy?
- A. Proxy network load balancer
- B. External passthrough load balancer
- C. External application load balancer
- D. Internal passthrough load balancer
Answer: B
Explanation:
An external passthrough load balancer forwards traffic without terminating sessions, preserving the original client connection, which is ideal for forwarding traffic directly to internal web servers.
NEW QUESTION # 29
......
FCP_GCS_AD-7.6 Free Certification Exam Material with 37 Q&As : https://pass4sure.practicedump.com/FCP_GCS_AD-7.6-exam-questions.html